


In this article:
- Section 1 with long heading text
- Section 2 with long heading text falling on to two lines
- Section 3 with long heading text
- Section 4 with long heading text falling on to two lines
Share this article


No practice expects to have a data breach, and a good share of the ones that happen come down to something ordinary: an email to the wrong address, a laptop left somewhere, a login that got shared. What makes the difference on the day is having decided what you will do before you need to. The plan itself is short. Your practice contains what happened, records it and works out whether the law requires a report. If it does, the Notifiable Data Breaches (NDB) scheme makes you notify the Office of the Australian Information Commissioner (OAIC) and the affected patients, then close the gap.
Your data breach response plan runs in five steps:
- Contain: Revoke or change the access that let it happen, without destroying evidence
- Record: Note who found it, when, what information, and how
- Assess: Work out whether it meets the test for an eligible data breach
- Notify: Give the OAIC a statement and tell affected patients
- Review: find what let it happen and close the gap
Four come from the OAIC's quick reference guide for responding to a data breach with the added record step, though the regulator's own plan puts it first.
The first three overlap more often than they queue, and telling patients first is sometimes right. Current as of August 2026.


Contain Record Assess Notify Review
Now name the person for each step, and a deputy for each. In a practice of five to fifteen people that is usually the practice manager for contain and record, and the owner or principal for assess and notify. The OAIC says as much: in a small entity the owner or principal may be the one who has to act. Writing that down is the whole job. You do not need a consultant, a lawyer or an incident response firm to do it, and the plan only helps if it exists before the day you need it.
If you run more than one site, this is one plan with one named person, not one per location. A breach at any site is the practice's breach. Jump to the first hours, when you must notify or the printable plan.
Most owners assume this is a big-business problem, or one that starts above a turnover threshold. It is neither. The OAIC's small business turnover threshold is $3 million a year, and plenty of practices sit under it, but a business that provides a health service and holds health information outside an employee record is covered whatever its turnover (ss 6FB, 6D(4)(b)). The OAIC names a dentist among its examples. The Privacy Act obligations behind the NDB scheme are yours.
In the OAIC's own health-sector breach data for July to December 2025, health providers spotted 86 breaches within ten days, faster than any other top-five sector. On the same dataset, 41 notifications took more than 30 days to reach the regulator. Time to notify there is not the statutory clock, so a longer gap is not automatically non-compliance. Noticing is not this sector's weak point. Responding is.
There is a legal edge to that. Remedial action taken fast enough means a breach "is not, and is taken never to have been" an eligible data breach at all (s 26WF(1)). Speed changes the legal outcome, not only its size.
What do you and your team do in the first hours after a breach?
Change or remove the access that let it happen, write down what you find as you go and take care not to wipe the evidence you will need later. Shutting the whole system down isn’t generally the right move, and rarely even possible for a practice whose records live in a browser.
The OAIC's own data breach response plan says: "Our actions in the first 24 hours after discovering a data breach are crucial to the success of our response."The regulator is describing itself there, not setting you a rule. Avant's guidance for practices responding to a data breach lands on the same window, recommending a plan that lets you respond within 24 hours. Neither is a legal deadline.
The regulator's containment guidance already allows for a practice without a server room: where shutting down is impractical or would lose evidence, revoke or change access privileges instead. In a small practice that person is usually you, which is why the names go on the plan in advance.
Three things make that quick:
- An exportable record of changes: Who changed or deleted what, when, with the before-and-after values, for the patient record involved
- Permission levels you can tighten immediately: Setting a user to no access removes them while their activity record stays intact, revoking access and preserving evidence in one action
- Approved locations and login windows: Control where and when anyone can sign in while you work out what happened
That is audit trails and access controls in Dentally, and it is the part worth knowing in advance: most of what an assessment asks you to produce is already being recorded as you work. Software supports your compliance. The legal duty stays with the practice.
When must you notify the OAIC and your patients?
It becomes an eligible data breach when all three parts of the OAIC's three-part test are met:
- Unauthorised access, disclosure or loss of personal information
- Likely serious harm to one or more people, as a reasonable person would see it
- Remedial action has not prevented that likely risk of serious harm
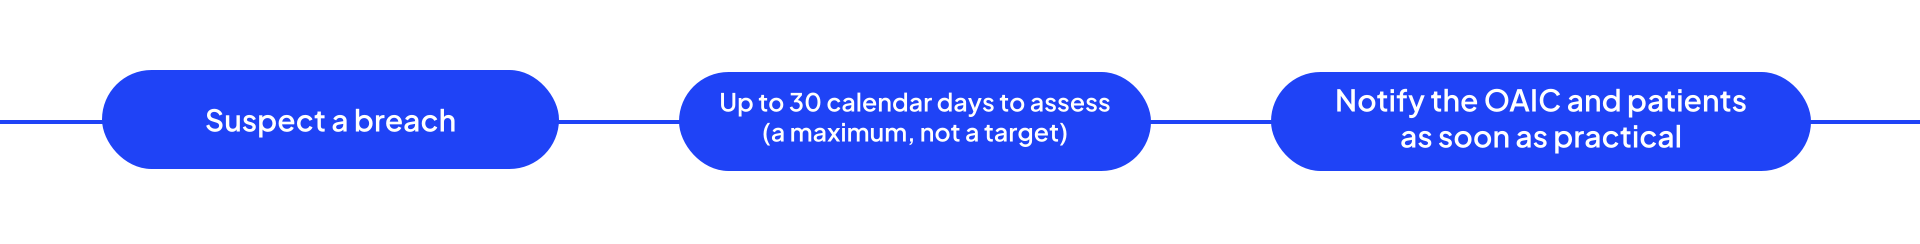
Once you have reasonable grounds to believe it does, the standard is "as soon as practicable", not a set number of days. Before that, a different clock runs.
A notifiable data breach is one you must report under the Notifiable Data Breaches scheme in Part IIIC of the Privacy Act.
The third part of this test is where speed pays. Under the Privacy Act's notifiable data breach provisions, remedial action that prevents the likely risk of serious harm takes the breach outside the scheme (s 26WF(1)). That can hold for some patients and not others.
Two clocks run. The OAIC's guidance on the notifiable data breaches scheme sets the first: all reasonable steps to complete a reasonable and expeditious assessment of a suspected breach within 30 calendar days. The Commissioner treats that as a maximum rather than a target. The second is "as soon as practicable", twice over. Your statement goes to the Commissioner after you become aware (s 26WK(2)), and you tell patients after that statement is finished (s 26WL(3)).
The statement is short: your identity and contact details, a description of the breach, the kinds of information involved, and what you recommend patients do (s 26WK(3)). How to report a data breach to the OAIC is where it goes, and patients get the same four things by one of three routes: everyone involved, only those at risk, or, if neither is practicable, a published statement you actively publicise (s 26WL(2)).
The OAIC's first civil penalties under the Privacy Act came in three parts. Two were for the response: one for failing to assess, one for failing to give the Commissioner a statement as soon as practicable. The third covered the security failure. The Privacy Commissioner singled out providers operating within Australia's healthcare system.
What are the types of data breaches dental practices face?
Four shapes cover most of what a dental practice will actually meet: a device is lost or stolen, a system is hacked, information goes to the wrong person, or a staff member opens a record they had no work reason to open. In a practice that is a laptop taken from reception, a compromised email account, or a referral letter sent to the wrong recipient. The OAIC's first example of unauthorised access is "an employee browsing sensitive customer records without any legitimate purpose", so the insider case is no outlier.
Of the 128 health-sector notifications the OAIC recorded from July to December 2025, 64 came from a malicious or criminal attack and 51 from human error. Attackers are the bigger share. Your own team is close behind.
What counts as security compliance for a dental practice?
Security compliance for a dental practice runs through Australian Privacy Principle (APP) 11 of the Privacy Act: take reasonable steps to protect the personal information you hold. Data breaches are one of the nine areas the OAIC's guidance on reasonable steps under APP 11 says those steps should cover in all cases.
Reasonable scales in both directions: with the size and resources of the practice, and with how sensitive the information is. Dental records carry health information, which sits at the sensitive end. The steps are technical and organisational together: encryption and strong passwords, but also your policies, your training, and who can reach what. Breach response sits alongside the other eight areas inside a broader dental practice compliance checklist.
Is HIPAA relevant to Australian dental practices?
No. The Health Insurance Portability and Accountability Act (HIPAA) is United States law and it does not reach an Australian dental practice. What governs you is the Privacy Act 1988, the thirteen Australian Privacy Principles, and the Notifiable Data Breaches scheme in Part IIIC of that Act. HIPAA appears nowhere in the Privacy Act. The confusion is fair enough, because most dental breach content online is American.
How do you make a breach less likely?
Hold less patient data than you need, control who inside the practice can reach what and train your team on the mistake the Australian figures say actually happens. That is most of prevention in a small practice, and the order matters.
The Australian Signals Directorate's advice on securing customer data starts before the technical controls. Register the personal data you hold, limit what you collect and delete what you no longer need. Clinical records carry retention minimums in some states, so that last one means the old marketing list rather than the chart. Review how you manage patient consent while you are there.
Access control comes next: strong controls still help after someone has got in on stolen credentials. Then training, because human error sat close behind criminal attack. Drill the wrong-recipient email.
Get the printable plan
The data breach response plan for dental practices prints the whole thing. You get the five steps as a checklist, with the OAIC's four mapped alongside. There is a role grid with a blank for the person and their deputy, the real timings with their sections cited and a self-check against the three-part test. It follows the OAIC's checklist for what a response plan should cover, and it notes where the steps overlap.
Get the printable data breach response plan for dental practices.
Frequently asked questions
Five answers to what Australian practices ask most about breach response and the NDB scheme.
What should a data breach response plan include?
It should name what counts as a breach in your practice, who is on the response team and how you contain and assess one. It should also set out when you notify the OAIC and patients, and how you record and review afterwards. The OAIC publishes a checklist covering all of that, and the printable plan here follows it.
What are three things to be considered when assessing a data breach?
The OAIC names three: the type of personal information involved, the circumstances including its cause and extent, and the nature of the harm, including whether remedial action can remove it. Health information raises the risk on its own, because of what it reveals, so a dental record starts from a higher base than a mailing list.
What is a data breach response plan?
It is a document setting out the roles and responsibilities involved in managing a breach, and the steps your practice will take if one happens. Australian law does not require you to have one in writing. The OAIC treats it as a reasonable step for any entity holding health information, and expects it to reflect the scheme's requirements.
Does Australia have a 72-hour data breach rule?
No, not under the Notifiable Data Breaches scheme. That figure comes from European law and has no Australian counterpart. Under the Privacy Act you have up to thirty calendar days to assess a suspected breach, which the Commissioner treats as a maximum. Then you notify the OAIC and affected patients as soon as practicable (ss 26WH(2), 26WK(2), 26WL(3)).
What should you look for in a system that supports your breach response?
Ask any vendor for an exportable record of who changed or deleted what and when. Ask for permission levels you can tighten or remove immediately without wiping someone's activity history, and for controls on which locations and times staff can sign in from. If a vendor cannot show you all three, your breach response gets harder.
Print the plan, name the person who runs it, and keep it somewhere your team can reach without logging in. Still choosing software? The security page covers the containment side. Already with us? You can see how the patient's audit trail works in your own account, including how to export it.
Connect with us on social media
We'd love for you to join our online community. Stay up-to-date with our latest news, events, and content by following us on our social channels. We look forward to seeing you there!


